Description
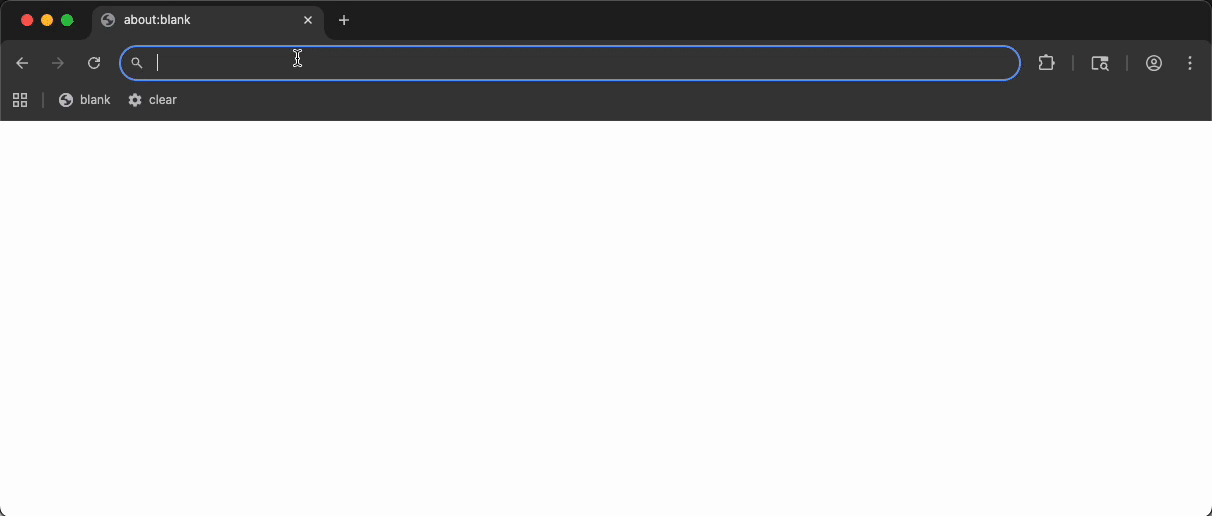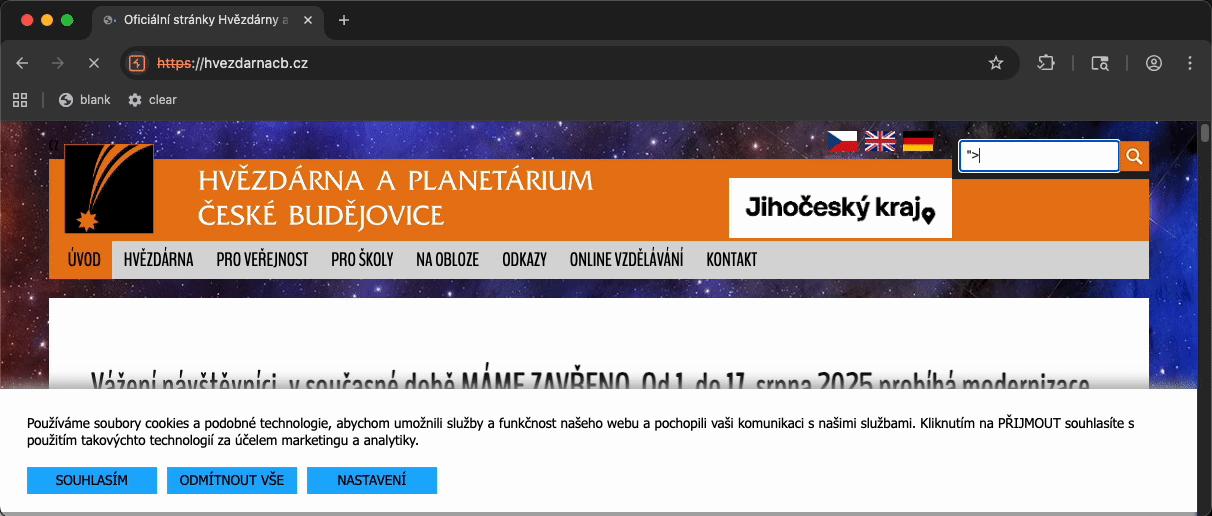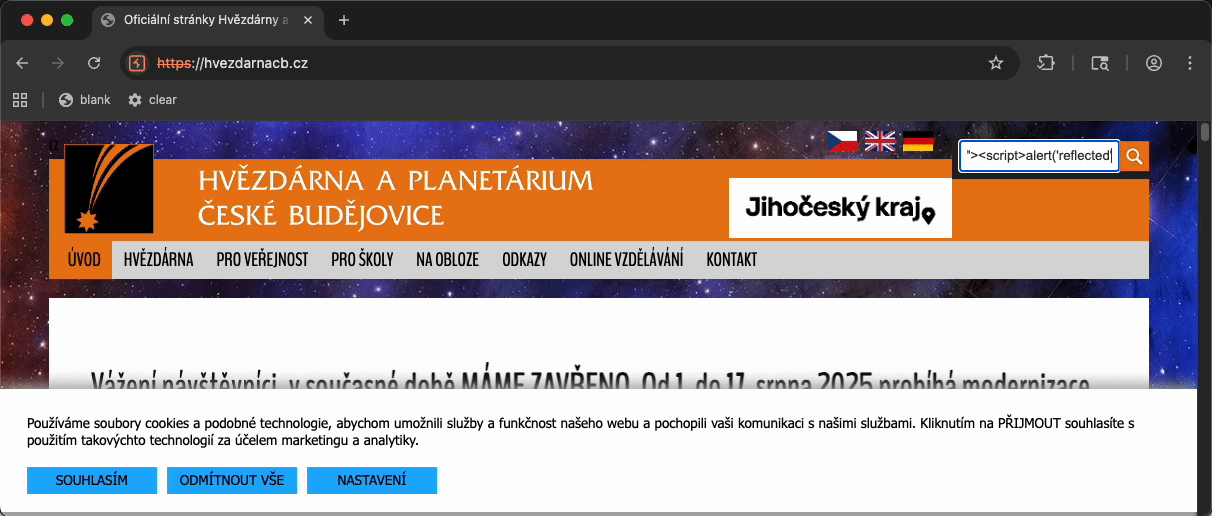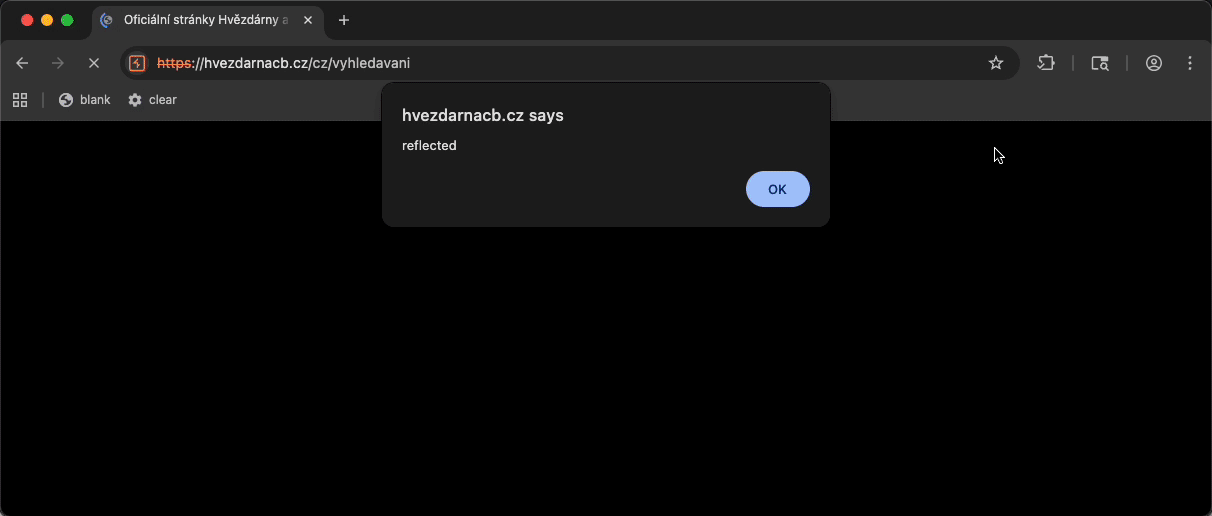
The search form returns the search term back into the page without encoding it. A crafted link can therefore run an attacker's JavaScript in the visitor's browser, as if it came from the observatory's own site. Affected: hvezdarnacb.cz, planetky.cz, klet.cz, klet.org and komety.cz.
Details
"><script>alert('reflected')</script><img src=x style=display:none onerror=null alt="
What a real, invisible attack could look like is shown in the deep dive on this finding.
Disclosure Timeline
17 November 2024 - vulnerability reported24 August 2025 - follow-up report resent9 June 2026 - follow-up report resent30 September 2026 - phone call with the IT department; a fix is not planned at this time